Using pfSense with LayerOne
Put public IPv4 on WAN, attach each private network as LAN or OPT, configure guest routes, and run NAT or DHCP in pfSense. The platform does not route between private networks.
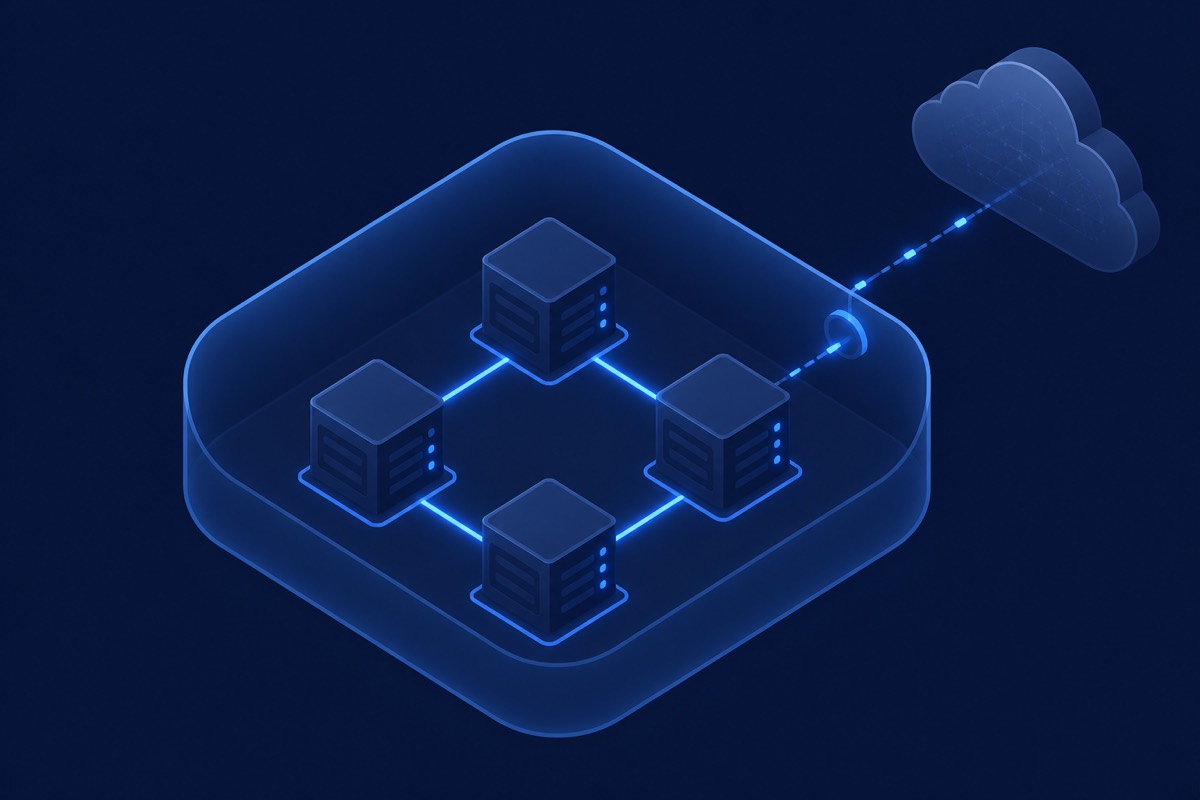
A LayerOne private network is an isolated L2 LAN. pfSense (or OPNsense, or VyOS) is how you put a WAN in front of it. NAT, DHCP, and VPN run in the guest. The platform does not SNAT the private network and does not route between two private networks on the same firewall.
Plan and image
no.appliance is the Network Optimized plan intended for a lightweight firewall. Choose a larger plan if you need more memory, storage, or inspection capacity. pfSense and OPNsense typically boot from a custom ISO; contact support if the image you need is not available. Keep public IPv4 on for the firewall itself.
Create the private networks first
Under Networking → Private networks, create each LAN you want the firewall to terminate. Example:
- Network A
10.10.0.0/24(LAN) - Network B
10.20.0.0/24(OPT1)
Leave each gateway blank until the firewall NICs exist. An account can create 10 private networks by default.
NICs: WAN, LAN, OPT
On a dual- or triple-homed firewall the usual mapping is:
- WAN (the first interface): the dedicated public IPv4. This is the only NIC with an internet path from LayerOne.
- LAN: network A. Assign a host address such as
10.10.0.1. - OPT1: network B. Assign
10.20.0.1. Add more OPT interfaces the same way for more private networks.
Your firewall may connect to multiple private networks. Configure client routes in each guest or advertise the gateway through pfSense DHCP. The portal's gateway field is an optional reference and does not configure clients.
Inside pfSense
Assign WAN to the public adapter, LAN to network A, and OPT1 to network B. Choose and configure each private interface address inside pfSense. Set the interface MTU to 1450 on every private-network adapter.
Enable the NAT, DHCP, VPN, and forwarding rules you need inside pfSense. Servers on one private network can already communicate with each other. Traffic reaches another private network or the internet only when your firewall explicitly forwards it.
Choose static addressing or DHCP
For fixed LAN addresses, configure the IP, subnet and gateway inside each guest. For DHCP, enable the DHCP client on the guest interface and run the server in pfSense. LayerOne does not allocate private addresses or write private Cloud-Init settings.
Configure WAN, LAN, and OPT inside the pfSense interface. No private IP is requested when you connect a network in LayerOne; set it inside pfSense.
Private-only workloads behind the firewall
Application and database servers can deploy without a public IP and connect only to a private network. Reach them through pfSense, another server on the same network, or the browser console. LayerOne does not provide NAT for them, and public IPv4 cannot be added after deployment.
OPNsense and VyOS
The same NIC layout applies. OPNsense: WAN / LAN / OPT, MTU 1450 on the private-network adapters, NAT and DHCP in the guest. VyOS: assign eth0 as the public WAN and later Ethernet interfaces to each private network, then set interfaces ethernet … mtu 1450 and your own NAT or routing. LayerOne still does not route between private networks.
Related
- Why configure a virtual network
- How to set up a virtual network
- Docs: firewall appliances
- Pricing (Network Optimized, including no.appliance)
Keep exploring
All articles →-
How to Self-Host Dawarich on a VPS
Run a private location-history timeline with Docker, PostGIS, Redis, background workers, HTTPS, and an off-server backup plan.
Read article -
How to Self-Host MicroBin on a VPS
Host a small paste and file-sharing service behind your own domain, require authentication, and keep its data off the public container port.
Read article -
How to Self-Host Gatus on a VPS
Build a lightweight status page from a YAML file, check HTTP and TCP services, and send alerts without running a full monitoring stack.
Read article